Website security, built on a proactive patching posture

The single biggest driver of site compromise is unpatched vulnerabilities in out-of-date plugins.  Cyber Shield SLA is SoBold's monthly patching baseline with proactive between-cycle patching whenever a high or critical vulnerability is disclosed, backed by real-time vulnerability monitoring across every site we manage.

The threat landscape has shifted. Talk to us about our Cyber Shield SLA

AI has industrialised attacks on websites, and ready-made exploit kits are widely available for attackers to scan, identify, and compromise vulnerable sites at scale, often within hours of a new vulnerability being publicly disclosed.

The volume and severity of attacks has escalated sharply, with the single root cause being out-of-date plugins with a known, published vulnerability that has not yet been patched.

The consequences range from site downtime and remediation costs through to end-user harm, including cases where attackers replaced the front-facing site with malware designed to compromise visitors’ own devices.

The exposure window

New vulnerabilities are being disclosed every day, and attackers now weaponise them within hours of disclosure, often before site owners are even aware there’s a risk.

The time between a vulnerability being disclosed and being patched on your site is your exposure window, and the longer this window stays open, the greater the risk.

The more frequently your site is patched, the smaller the window, the lower the risk.

Layering proactive patching between patching cycles enables high and critical vulnerabilities to be addressed the moment they’re disclosed rather than waiting for the next cycle.
Cyber Shield SLA

Cyber Shield SLA is SoBold’s proactive security posture, which combines a guaranteed monthly patching cycle with between-cycle patching for any high or critical vulnerability disclosed on your site.

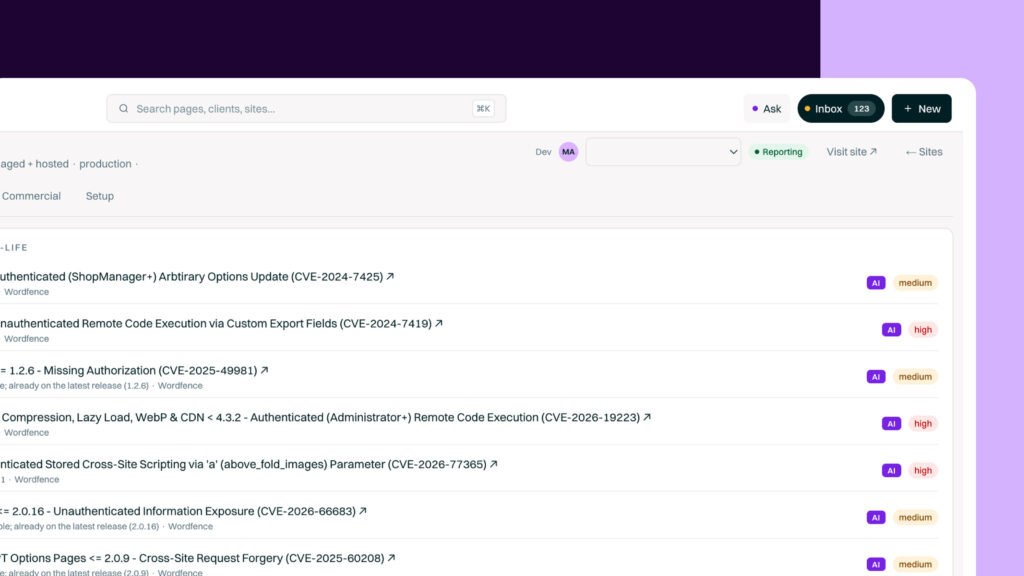
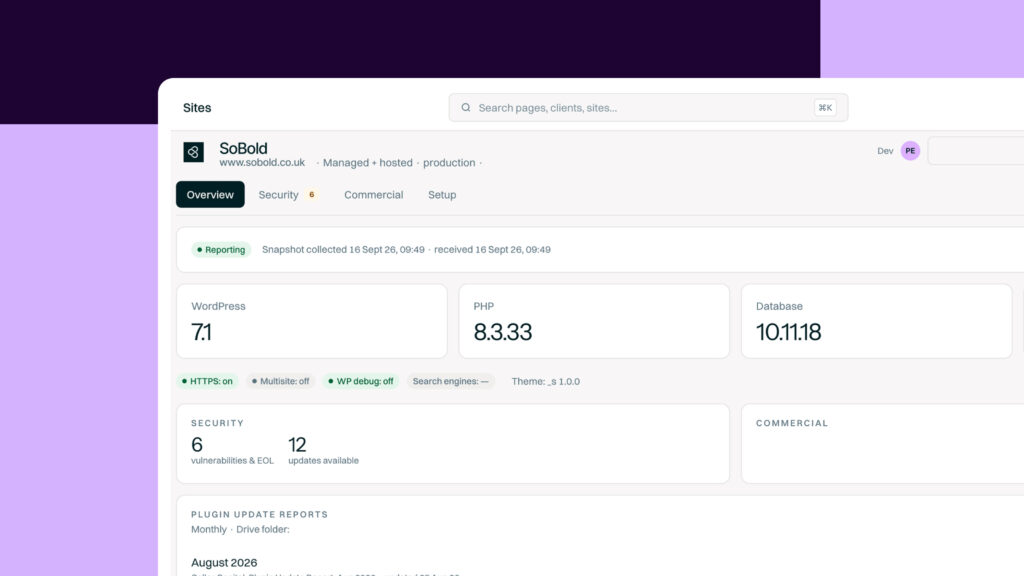
Our clients’ sites are all backed by real-time vulnerability monitoring through our internal security dashboard.

What’s included

The commercial outcomes of a well-built knowledge assistant vary by deployment, but tend to cluster around four things.

10 Tips to Improve WordPress Security and Minimise Risks

Monthly patching cycle

A guaranteed monthly cycle covering plugins, CMS hardening, and dependencies.

Every cycle is executed by a SoBold engineer, tested, and followed by a written report.

Proactive between-cycle patching

When a high or critical vulnerability is disclosed on your site, we patch it immediately with no cap on frequency and at no additional cost.

Real-time vulnerability monitoring

Every site on our Cyber Shield SLA is monitored through our internal SoBold dashboard, which checks against published CVE and vulnerability intelligence feeds at minimum daily intervals.

New vulnerabilities are surfaced and triaged the moment they’re disclosed.

A verifiable AI layer the business can stand behind

A written report at the end of every cycle details all patches applied from both the scheduled monthly cycle and any between-cycle patches performed in response to alerts.

Proactive vs reactive

Patching cadence

Quarterly / Bi-annual patching

Every 3 or 6 months

Cyber Shield SLA

Monthly baseline

Exposure window between cycles

Quarterly / Bi-annual patching

12–24 weeks unpatched

Cyber Shield SLA

Zero - proactively patched between cycles

Response to newly disclosed high/critical CVEs

Quarterly / Bi-annual patching

Deferred to next cycle

Cyber Shield SLA

Patched immediately, no additional cost

Vulnerability monitoring

Quarterly / Bi-annual patching

Ad hoc

Cyber Shield SLA

Real-time via SoBold dashboard

Reporting

Quarterly / Bi-annual patching

Post-cycle only

Cyber Shield SLA

Post-cycle plus alert-driven updates

Posture

Quarterly / Bi-annual patching

Reactive

Cyber Shield SLA

Proactive

How it works

When managing our clients with our Cyber Shield SLA we operate continuously in the background, with them having the knowledge that their site is patched and secure against high and critical vulnerabilities.

100+ Partnerships

Continuous monitoring

Your site registered on our vulnerability dashboard, which polls published CVE and vulnerability intelligence sources at least daily and cross-references them against every plugin, theme and core version installed.

Alert and triage

When a new vulnerability is disclosed affecting your site, it’s surfaced on the dashboard and assessed by a SoBold engineer against severity (medium / high / critical) and exploitability.

Patching

Medium-severity issues are addressed in the next scheduled monthly cycle.

High or critical vulnerabilities are patched immediately, between cycles, at no additional cost.

All patches are tested before deployment.

Reporting

Every action, scheduled or between-cycle, is documented in your monthly Cyber Shield SLA report, sent by your Digital Project Manager.

Cyber Shield SLA is included in the Maintain retainer

Cyber Shield SLA is the recommended security posture within our Maintain retainer, the ongoing support agreement that covers your site’s day-to-day management, from ad-hoc updates and small enhancements through to security patching.

Maintain retainers are configured around your team’s needs.

Cyber Shield SLA sits as the security layer within them, ensuring your patching cadence is never the weak point.

Cyber Shield SLA FAQs

Will Newland - SoBold founder

Get in touch with Will for more answers.

A site on a quarterly schedule is effectively unpatched for 12 weeks at a time. Any vulnerability disclosed within that window sits open on your site until the next cycle.

Given the current volume of AI-driven scanning and the speed at which new vulnerabilities are weaponised, we consider this posture high-risk regardless of the site’s profile or traffic level.

Ad-hoc patching is reactive – we alert you, you approve the work, we invoice, we patch.

It works, but it introduces delay and the cost is unpredictable.

Cyber Shield SLA removes both problems: patching happens immediately when needed, at a fixed monthly cost.

We use the standard CVSS severity ratings published alongside each CVE.

Critical vulnerabilities typically allow unauthenticated remote code execution or full site takeover.

High-severity vulnerabilities allow significant compromise but usually require some condition to be met (authentication, specific configuration).

Cyber Shield SLA significantly reduces risk, but no security posture can guarantee zero compromise.

If a compromise occurs, SoBold’s remediation work is quoted and delivered separately – but clients on Cyber Shield SLA are, by design, the least likely to require it.

Yes.

The patching cycle covers plugins, WordPress core and installed themes and dependencies.

Plugins are the most common attack vector, but nothing in the stack is excluded.

Work with our team to build and scale your bespoke requirements.

Once you submit the form one of our team will contact you to set up a meeting to clarify your requirements and build a quote.

Working with leading b2b clients

    Message sent

    Thanks for reaching out. We'll be in touch within one working day to confirm your call.